

There are dozens of free online tools that let current and prospective customers scan your business for security weaknesses. One of the most popular is a simple domain checker. Type in a domain name and, in about ten seconds, it tells the world how seriously that business takes email security.
That matters more than you might think:
Earlier this year Assuredly reviewed our own email security. To get our external scan results looking sharp, one item stood out on the to do list: BIMI. It took real time, expertise and patience, which is exactly why it is so hard for small businesses to get right.
So we have broken the whole journey down, step by step. Grab a coffee, this one is worth the read.
Brand Indicators for Message Identification (BIMI)displays your verified brand logo next to your emails in supported inboxes.
In plain English:

Brand trust: customers instantly recognise that the email really is from you
Harder to impersonate: scammers cannot simply copy your logo into the inbox, because it is tied to a verified certificate
Better scan results: BIMI is one of the items public domain checkers look for
Stand out: a logo in a crowded inbox gets noticed

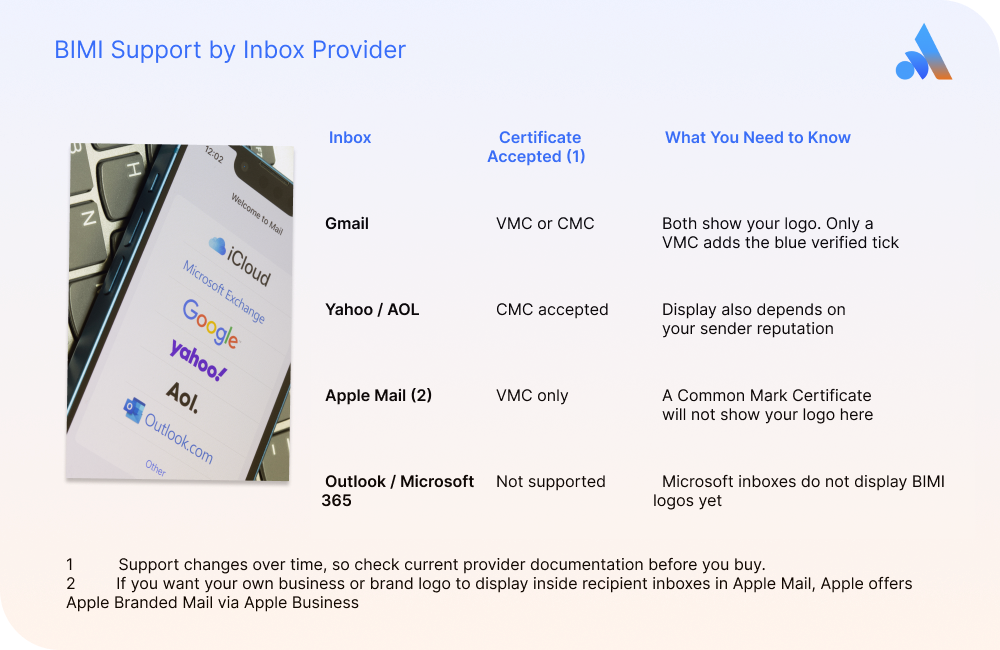
Not every inbox supports BIMI, and not every certificate works everywhere. Here is the current lay of the land.
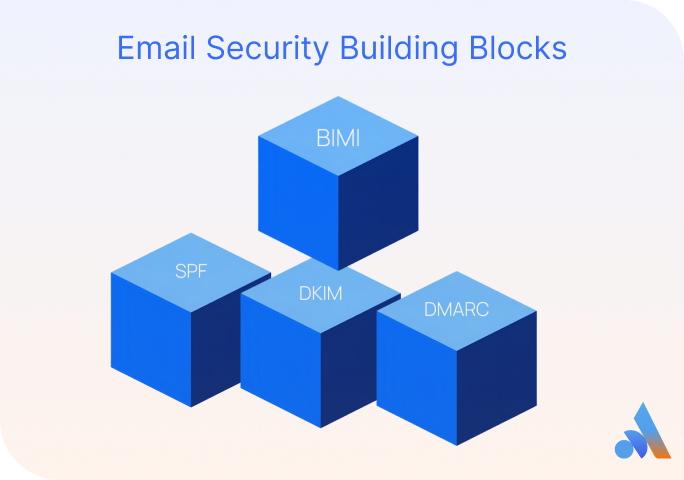
BIMI sits on top of your other email controls. It will not work unless the foundations are in place first.
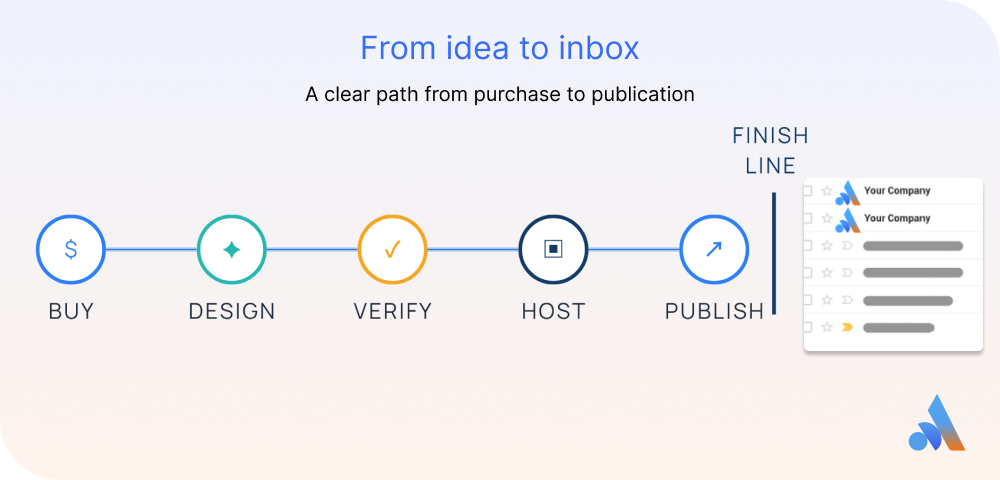
BIMI has more moving parts than most email controls, so here is the whole journey at a glance.
Then, as if by magic, your logo appears in supporting inboxes.
Verified Mark Certificate (VMC)
Common Mark Certificate (CMC)
We went with a Common Mark Certificate. Some providers also ask for evidence that your logo has been publicly used on your website for a period of time, so check this early.
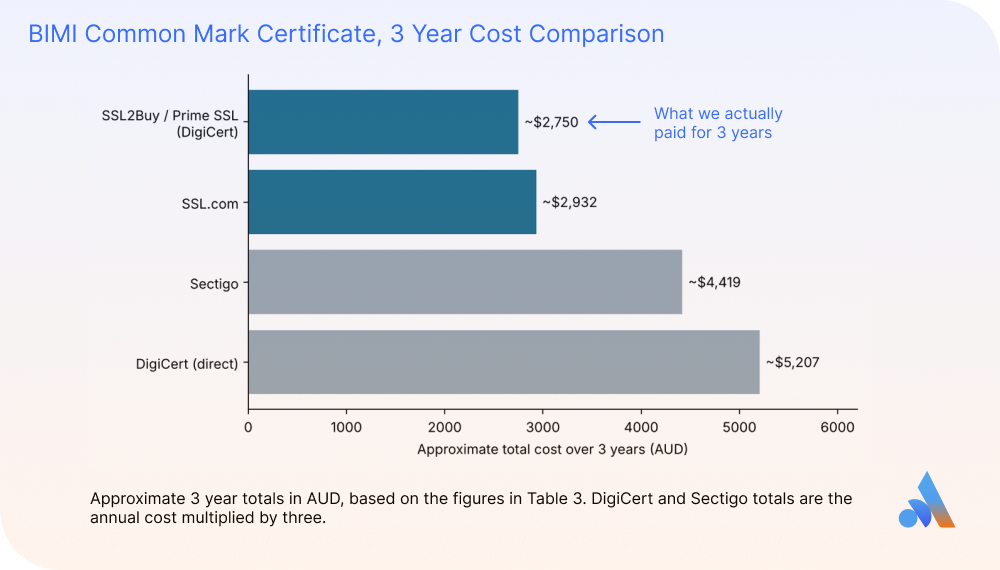
Here is what we found when shopping for a Common Mark Certificate. Treat these as a starting point and confirm current rates before you buy.
$2,750 AUD for 3 years, with forced PayPal fees
Watch out for forced payment processor fees
Check whether pricing is quoted in USD or AUD before you commit
Compare the multi year price, not just the headline annual rate
Resellers can be much cheaper for the exact same underlying certificate
This is the fiddly bit. Your logo needs to meet strict technical rules before it will be accepted.
This was a frustrating experience and even afterfollwing all the rules and steps below as our logo has gradients we needed specialist support which our certificate provider gave us in the end (thank you SSL2Buy!).
BIMI providers are picky about file formatting. Your final file must use LF line endings only.
Once this is done, your logo file is technically ready and you can submit it with your certificate application.
Once you upload your tiny SVG to your certificate provider's portal, they will get in touch to arrange an identity verification video call.
In our case, our Director had to:
It is a genuinely unusual ten minutes of your week, but it is a one off. And it is exactly what stops someone else from faking your brand's logo in other people's inboxes.

Your verified logo file must be hosted somewhere publicly accessible over HTTPS
In our case, our certificate provider hosted it for us (thank you again SSL2Buy), which made this step easy
If you host it yourself, make sure it is accessible.
Add a TXT record to your domain's DNS settings. Your certificate provider will give you the exact value to use.
Example BIMI DNS Record
And that's it. Once it propagates, your verified logo starts appearing next to your emails in supported inboxes.
If you would like a hand reviewing your email security posture, or understanding how controls like BIMI fit into your broader assurance program, get in touch with the Assuredly team. We have been through it ourselves, so you do not have to learn the hard way.

At the helm of our privately owned, global RegTech firm are industry experts who understand that security controls should never get in the way of business growth. We empower companies large and small to remain resilient against potential threats with easily accessible software solutions for implementing information security governance, risk or compliance measures.
We don't just throw a bunch of standards at you and let you try and figure it out! We have designed a thoughtful way of supporting all businesses consider, articulate and develop security controls that suit the needs of the organisation and provide clever reporting capability to allow insights and outcomes from security assessments to be leveraged by the business and shared with third parties.
Our platform places customers at the heart of our design process, while providing access to expert knowledge. With simple navigation and tangible results, we guarantee that all data is securely encrypted at-rest and in transit with no exceptions – meeting international standards with annual security penetration testing and ISO 27001 Certification.
